PhonePe Android Forensics
Offline, read-only analyser that turns an extracted PhonePe Android data folder into transactions, chat, contacts, a split ledger, a timeline and findings.
- License: MIT
- Android
- Mobile
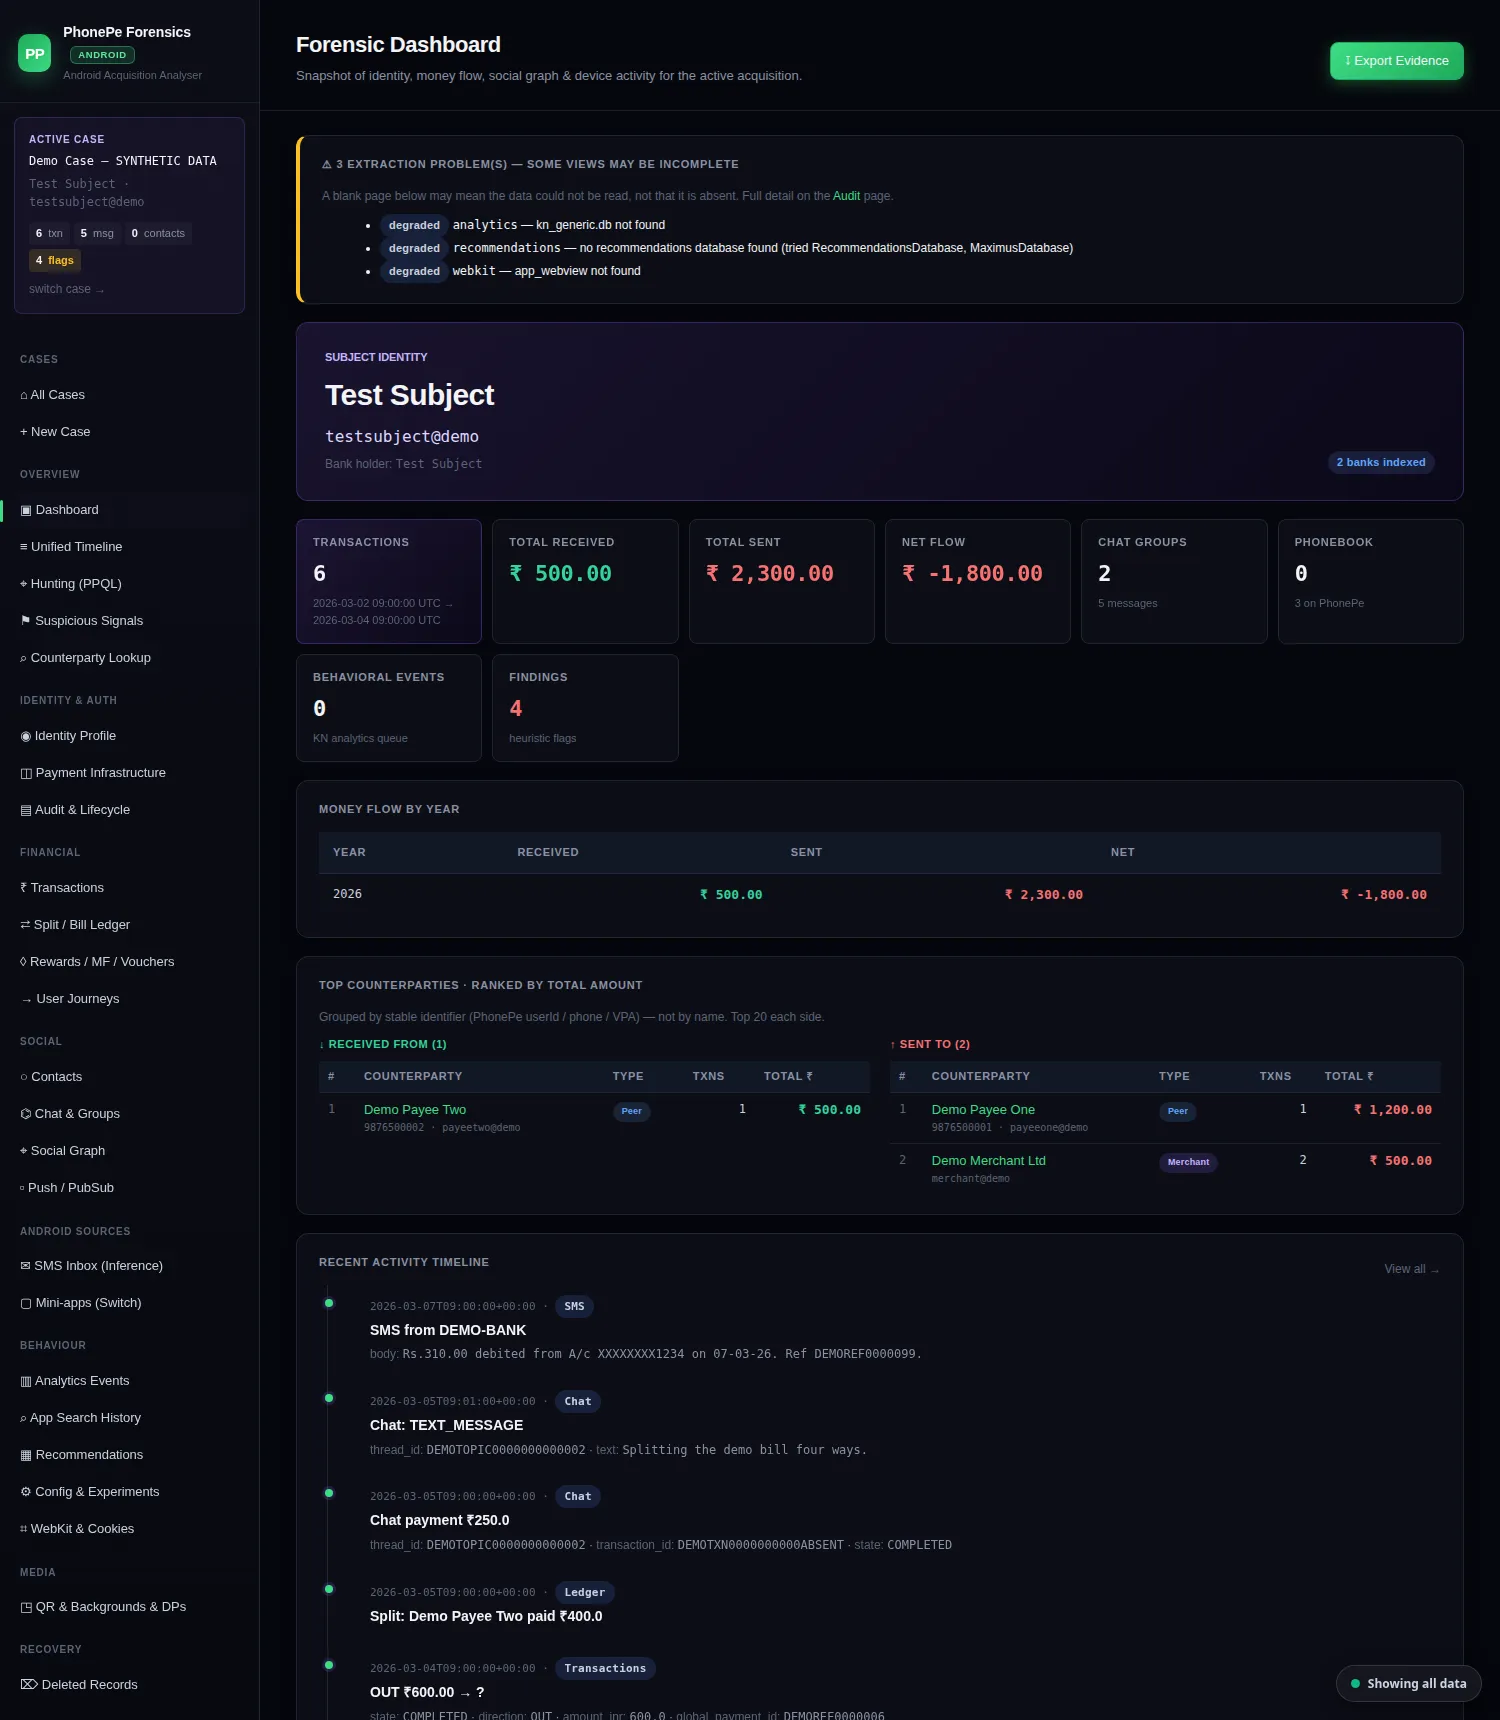
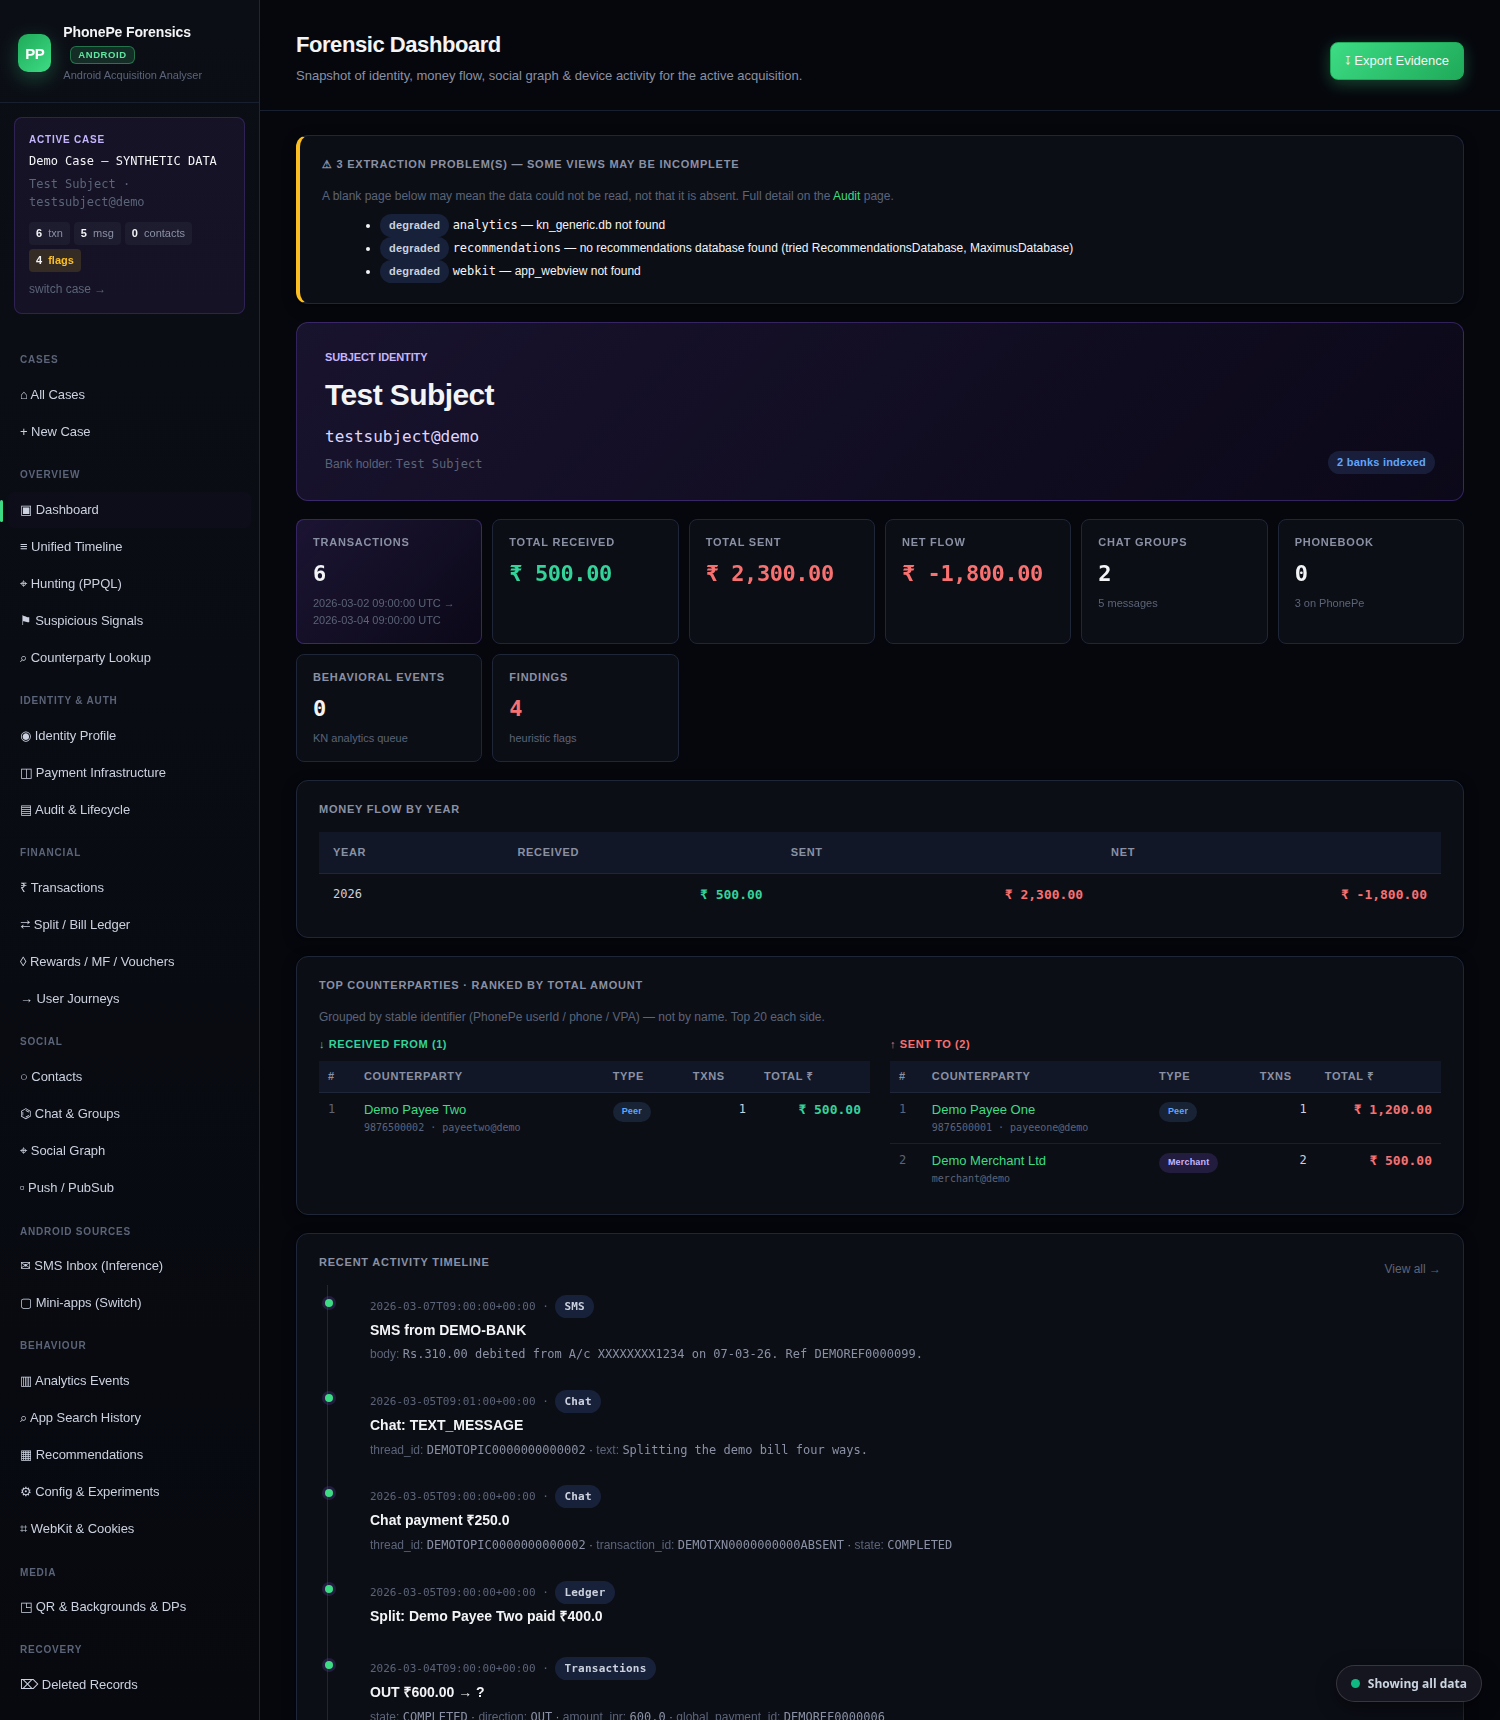
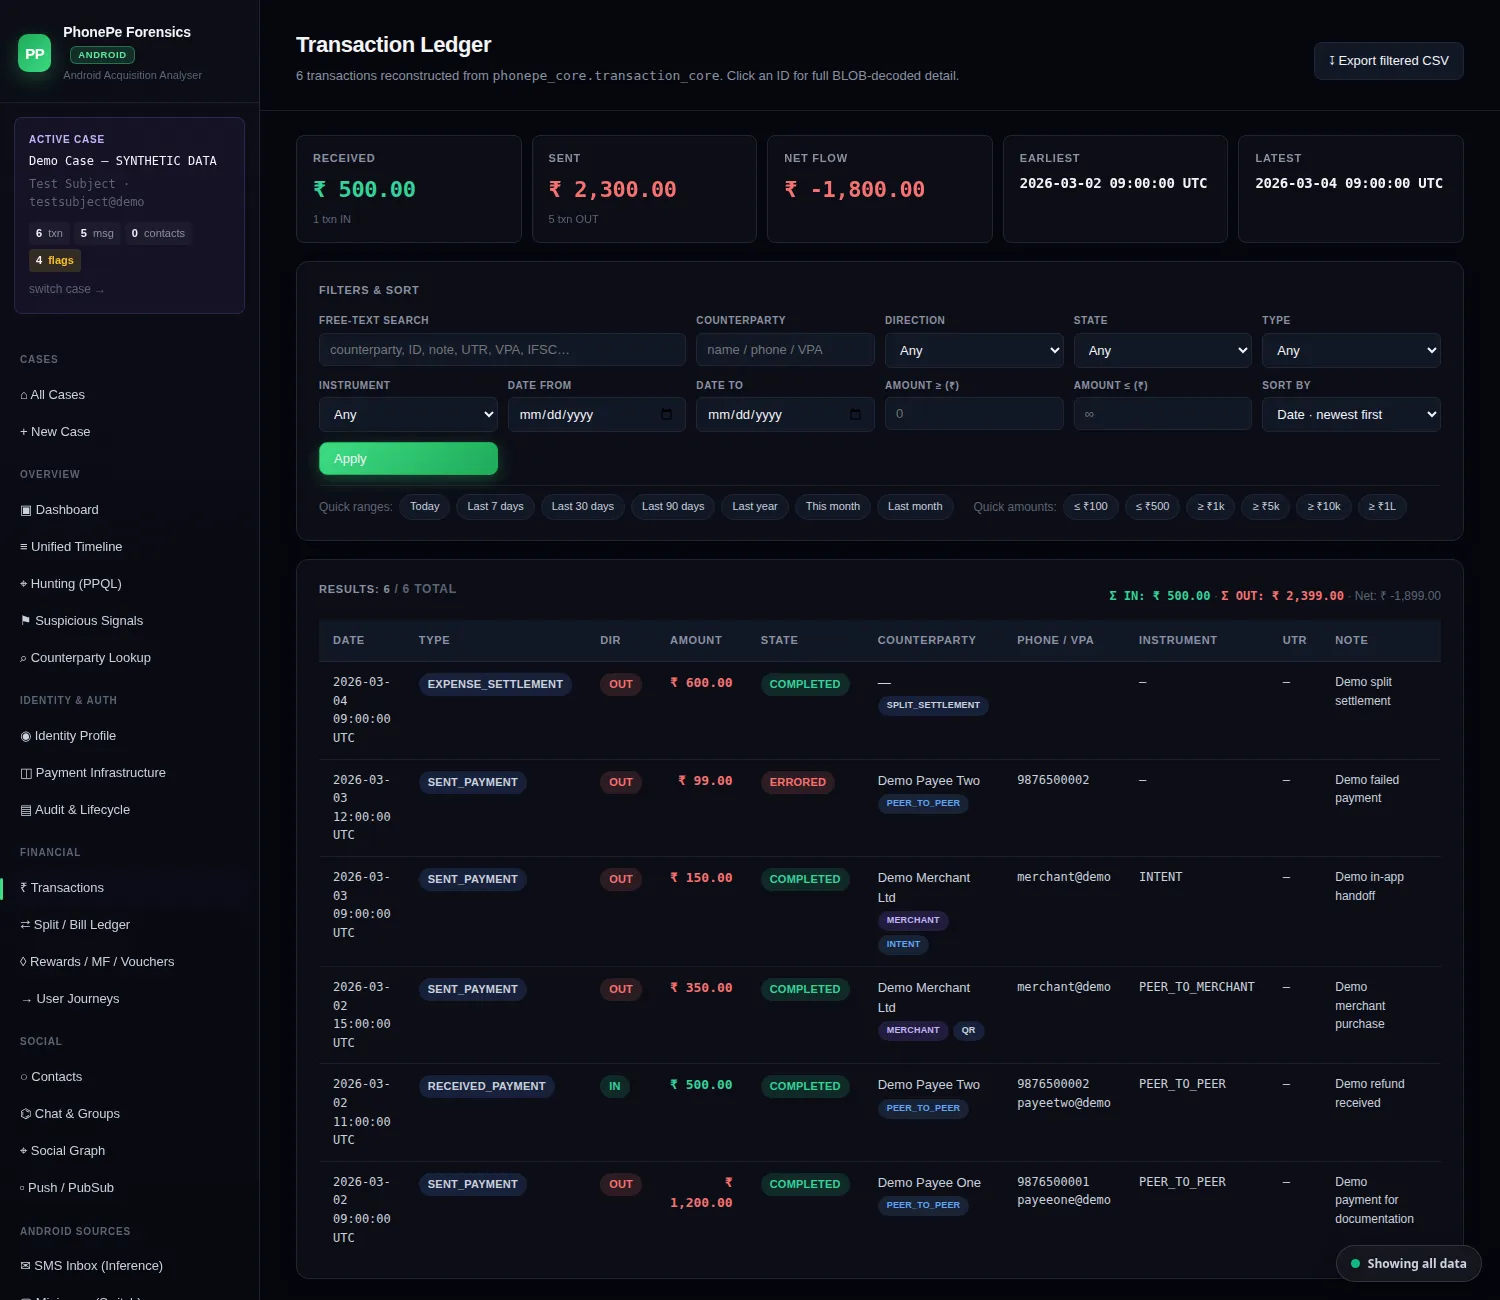
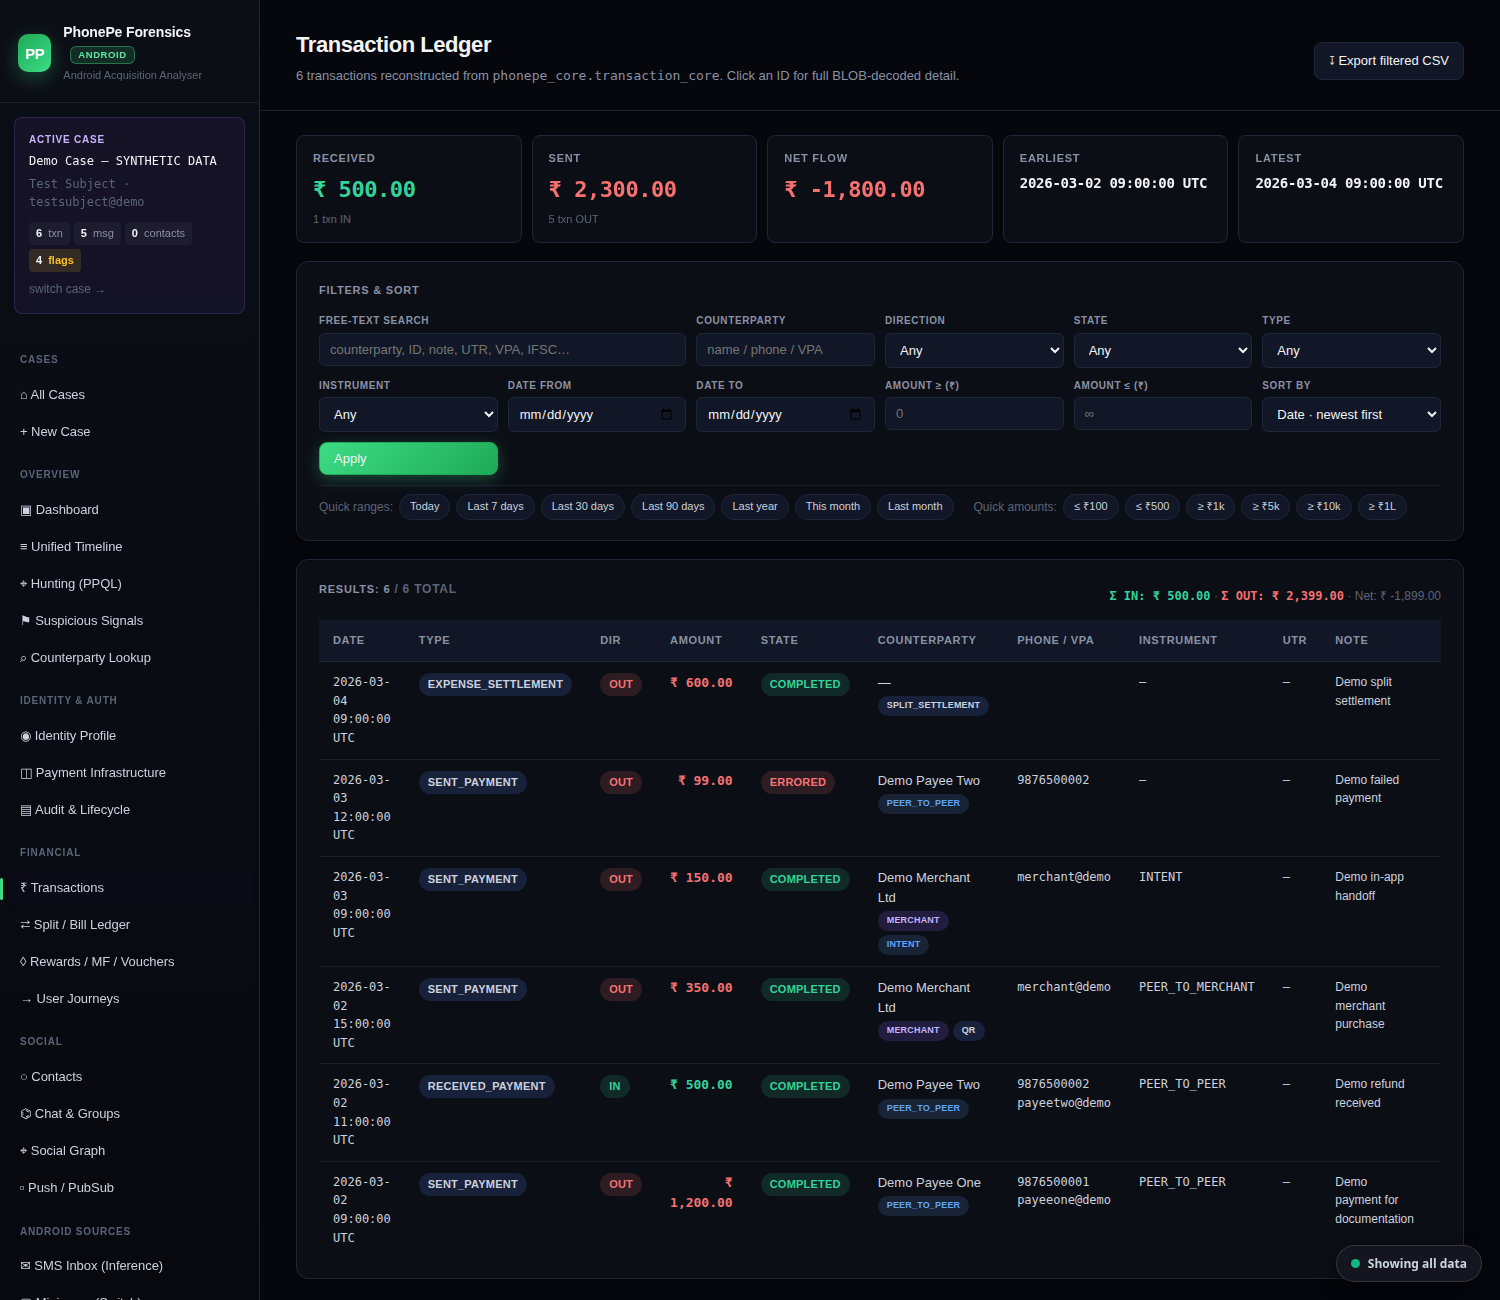
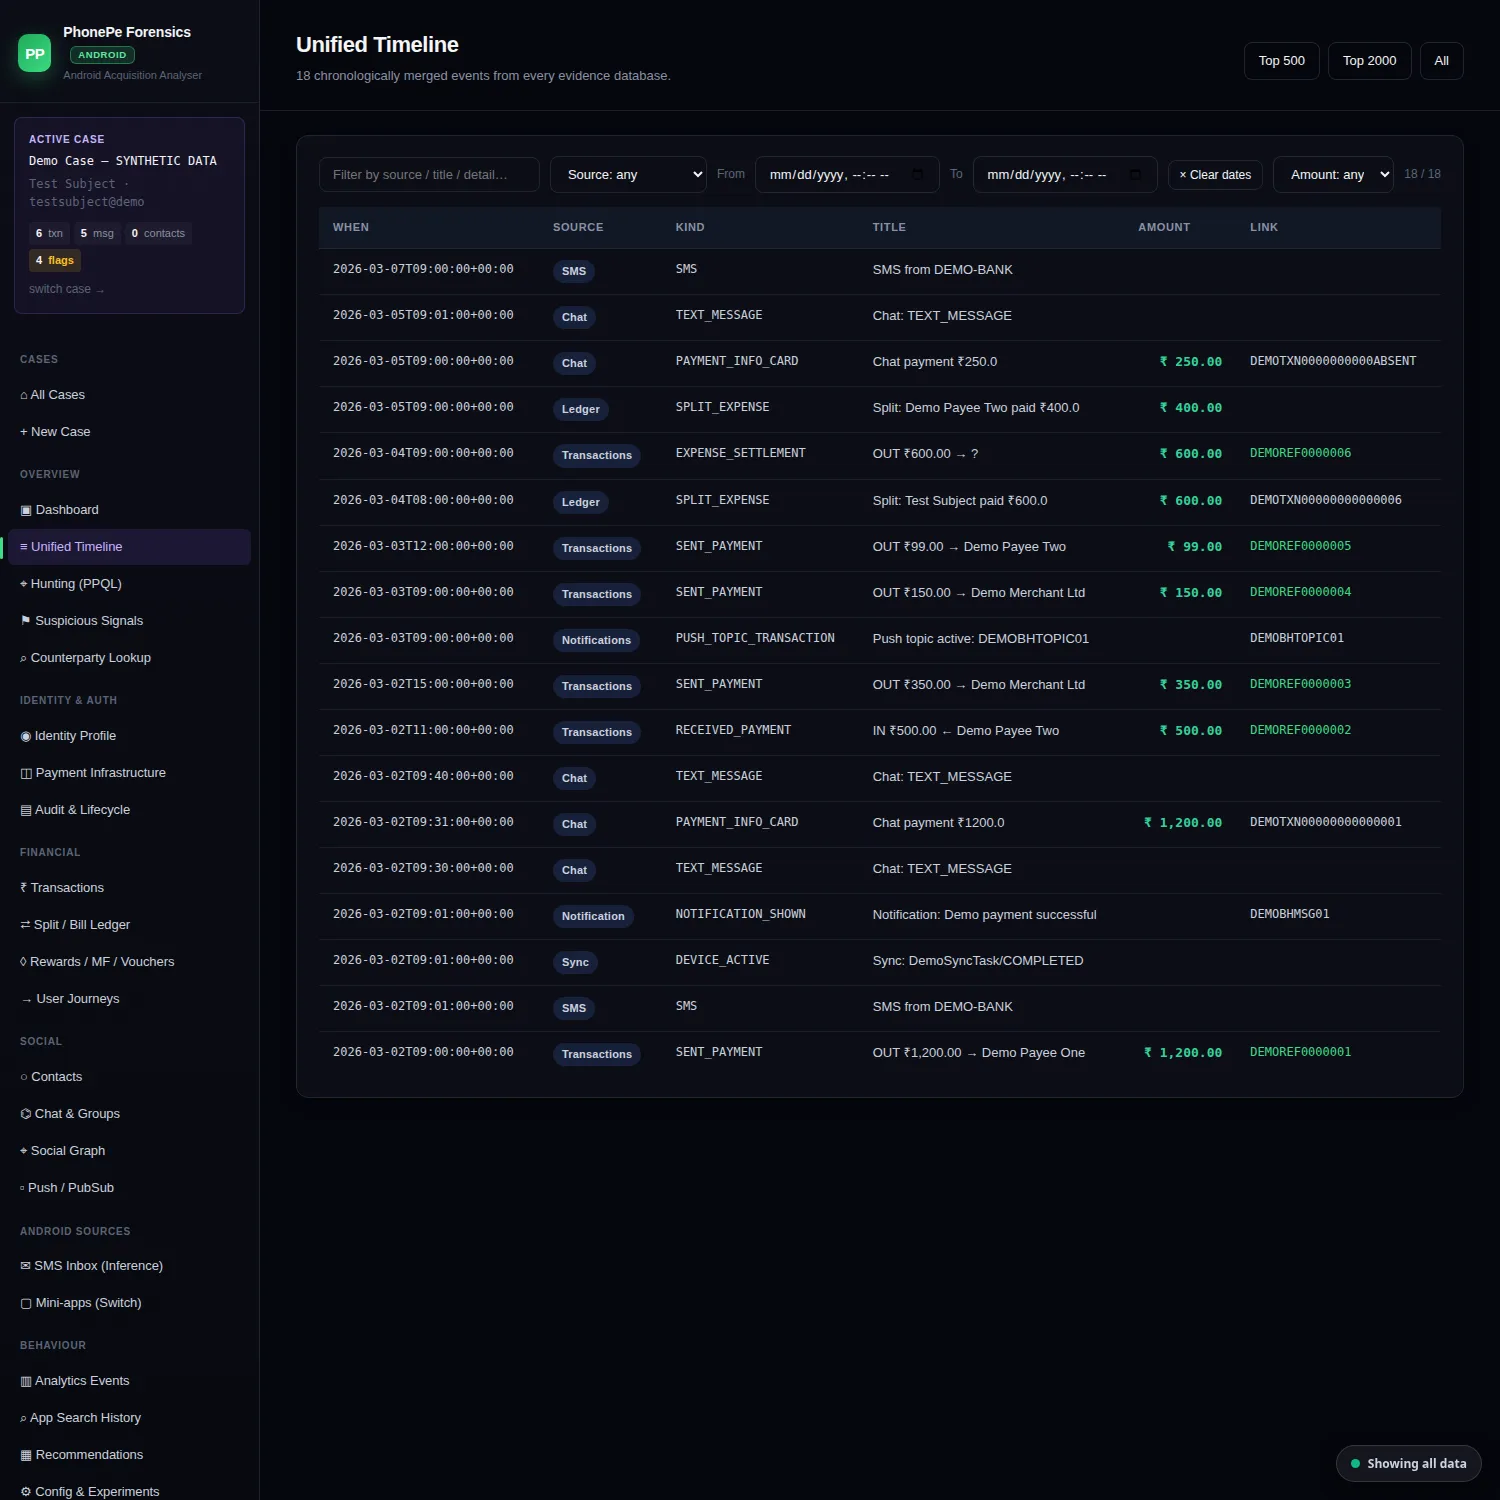
PhonePe Android Forensics is an offline analyser for data from the PhonePe Android app (com.phonepe.app). Point it at an extracted app data folder and it reconstructs transactions, chat, contacts, the split and bill ledger and identity into a unified timeline, a social-financial graph and suspicious-signal findings, shown in a local browser interface with the source of every field one click away.
It is read-only by construction: the evidence folder is hashed before parsing and never written to.
What it is, and is not
Section titled “What it is, and is not”It is an analysis tool: you give it data already extracted from a device, and it parses, correlates and presents it, showing its working. It is not an acquisition tool. It does not talk to phones, root devices or pull data; use a forensic extraction tool or ADB on a rooted device first.
What it surfaces
Section titled “What it surfaces”| Area | What you get |
|---|---|
| Transactions | Amount, direction, counterparty, instrument, UTR, merchant, state, initiation mode |
| Chat and groups | Threads, messages, payment cards, participants with recovered identities |
| Contacts | PhonePe contacts and the device phonebook, linked to each person’s chat |
| Split and bill ledger | Shared expenses, per-member shares, net balances, settlement-to-transaction links |
| Identity | Registered name and VPAs, device fingerprint, persistent IDs, sessions, location hints |
| Payment infrastructure | Linked accounts, VPAs, PSP handles, cards, wallets, mandate approvers |
| SMS and notifications | Bank SMS matched against transactions; decoded push notifications |
| Derived views | Unified timeline, social graph, suspicious-signal findings, counterparty profiles |
| Raw layer | Every table (browsable and exportable), shared preferences, files, and a read-only SQL console |
| Provenance | The database, table and column, or JSON path, behind every field shown |
How it stays reliable
Section titled “How it stays reliable”- Hashed before parsing. Every database and its
-wal,-shmand-journalfiles get a SHA-256 before anything is read. - Never written to. Databases without a write-ahead log are opened with SQLite’s
immutableflag; databases with one are copied to a scratch folder and recovered there, so WAL records are included without touching the original. - UTC throughout. All timestamps are UTC, and values outside 1973 to 2100 are rejected rather than shown as plausible dates.
- Exact identity recovery. Masked counterparties (
******1478) are resolved only by exact cross-table matches, labelled as recovered, and left unresolved when more than one contact fits. - Deleted-record recovery from SQLite free pages, free blocks, page slack, superseded WAL pages and rollback journals, excluding rows still present in the live table. An empty result is never presented as proof that nothing was deleted.
- Schema drift reported. Columns missing from a newer PhonePe schema come back empty and are listed on the Audit page instead of failing silently.
Requirements
Section titled “Requirements”| Item | Requirement |
|---|---|
| Python | 3.9 or newer |
| Packages | Flask |
| Input | The com.phonepe.app data folder from a full-filesystem or rooted extraction |
| Network | None; it runs locally and binds to 127.0.0.1 |
python run.py 127.0.0.1:8754Next steps
Section titled “Next steps”- Install PhonePe Android Forensics.
- Usage: cases, screens, PPQL queries and exports.
- Changelog.
Credits, source and license
Section titled “Credits, source and license”The tool was inspired by and built on Sujay Adkesar’s PhonePe-Forensics for iOS, vendored at upstream commit 007473a and reduced to an Android-only distribution. The repository states a plan to merge it back upstream into a single tool for both platforms.
It is open source under the MIT License. Source code and the full reference are on GitHub.